Stop .env leaks and malicious terminal commands before they run.
Coding agents read files, run commands and push to repositories. AvertGate inspects those actions on the developer’s machine: secrets do not leave, and no force push reaches a protected branch.
 GitHub · git push --force stopped
 Slack · production deploy awaiting approval
 Docker · malicious command stopped
Runs in front of the tools developers already use
 Cursor
 GitHub Copilot
 VS CodeGitHubDocker
 Kubernetes
 Antigravity
 Vercel
 Supabase
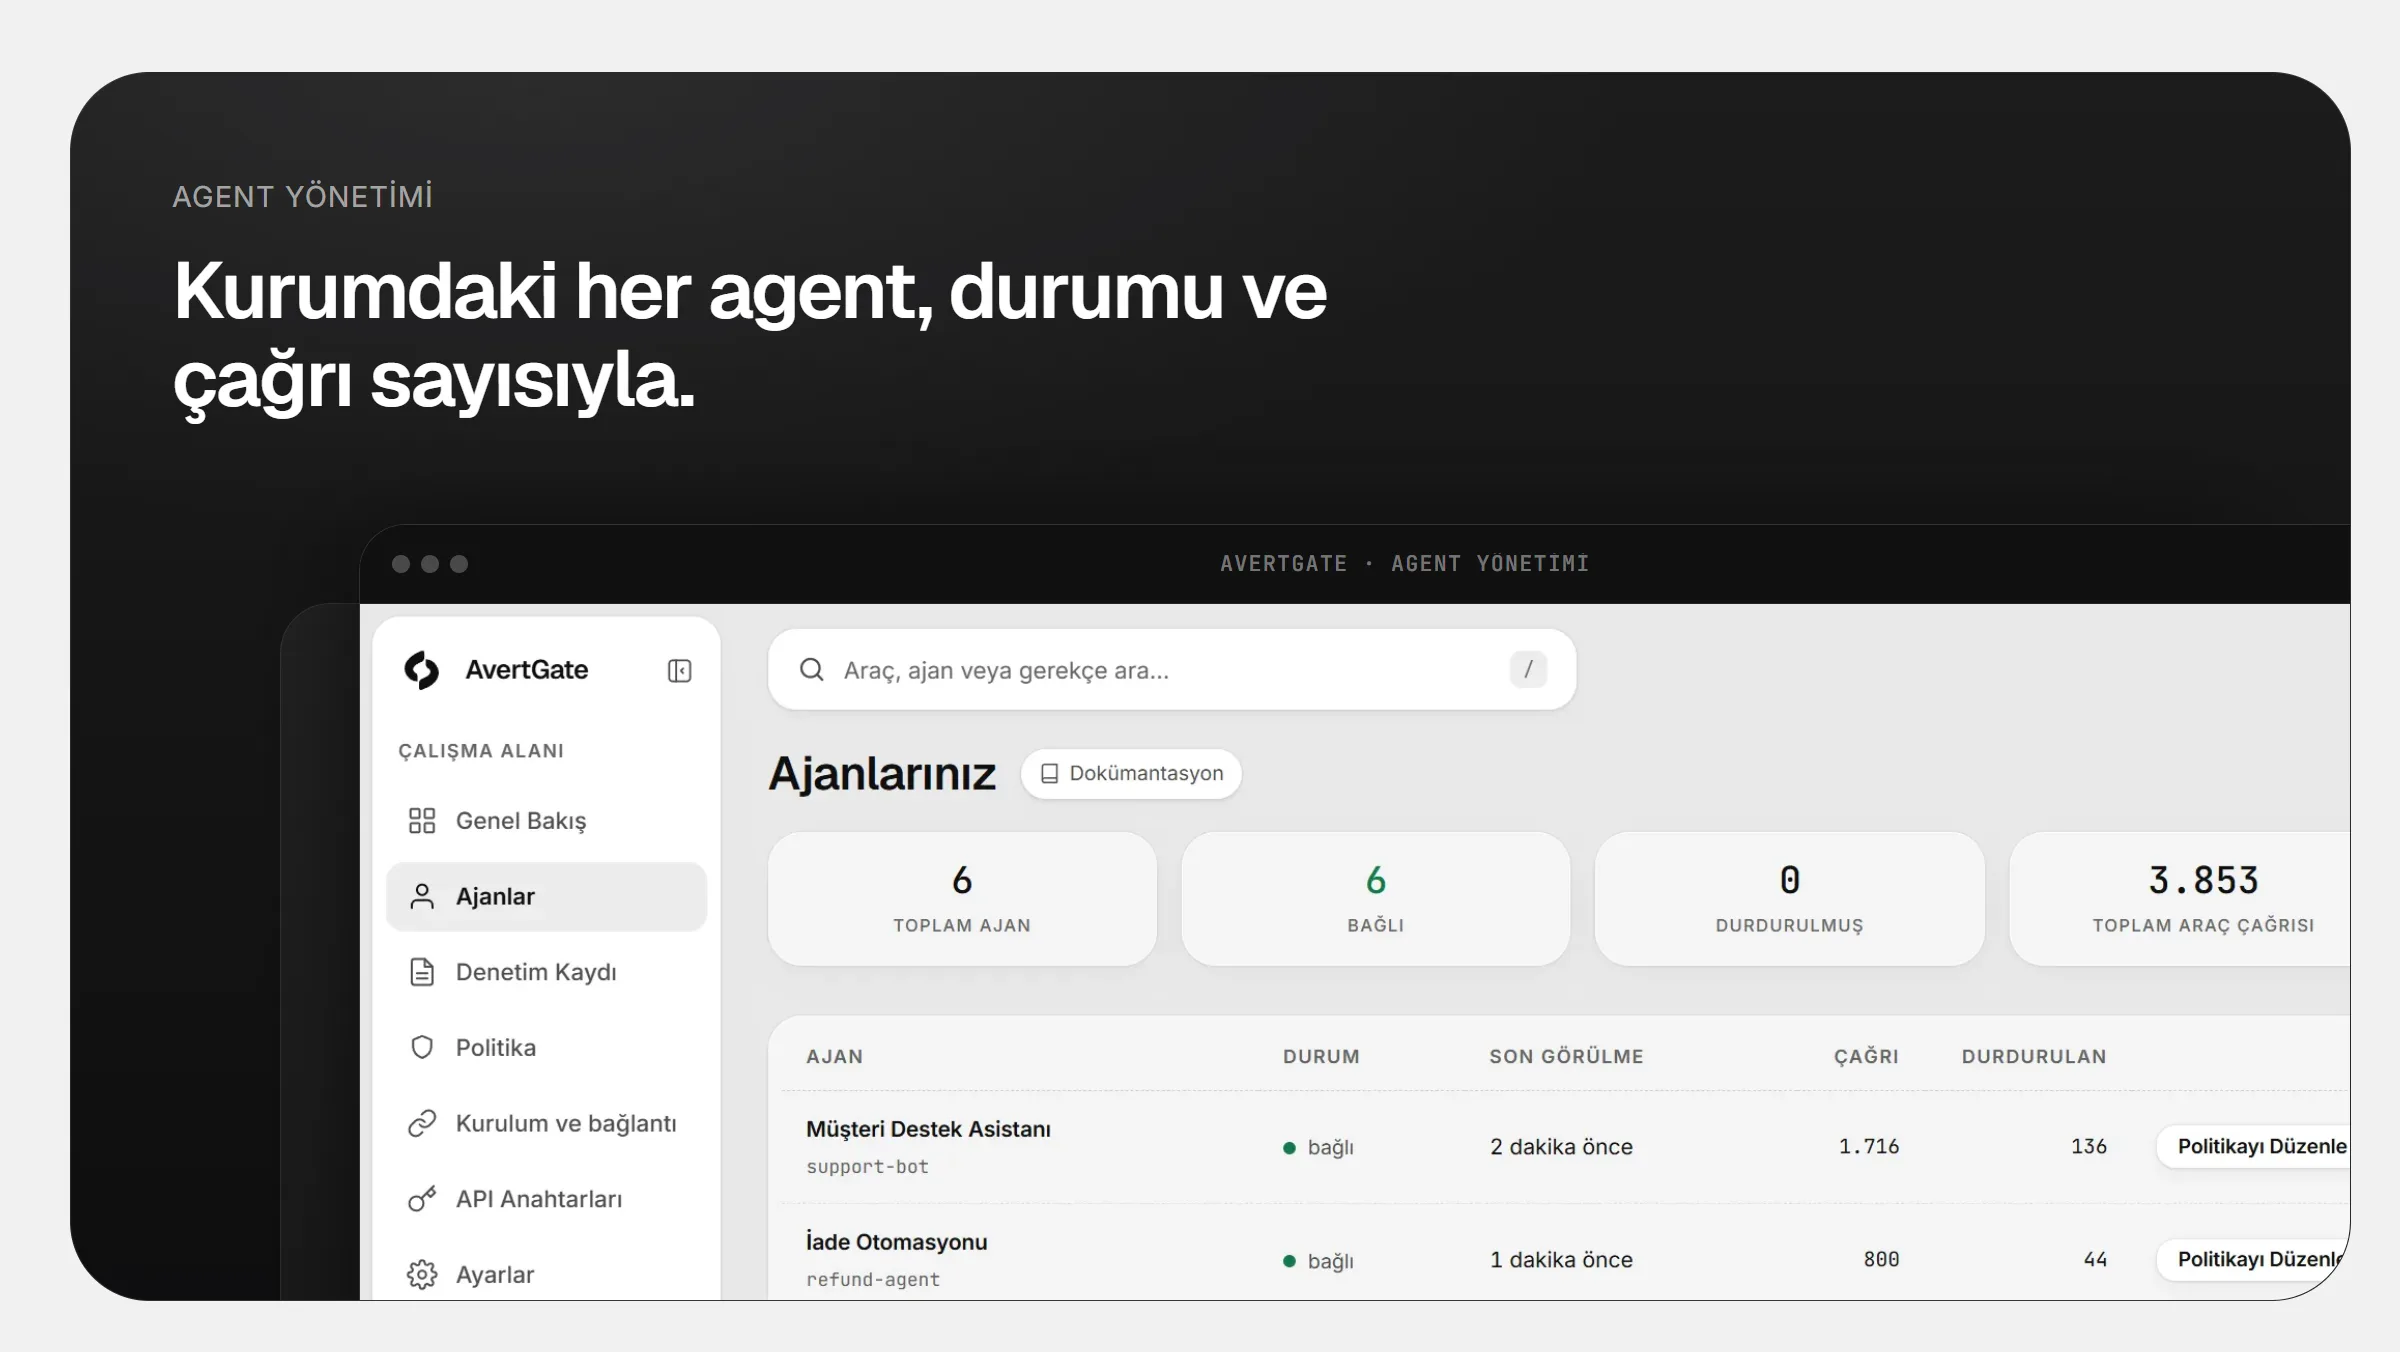
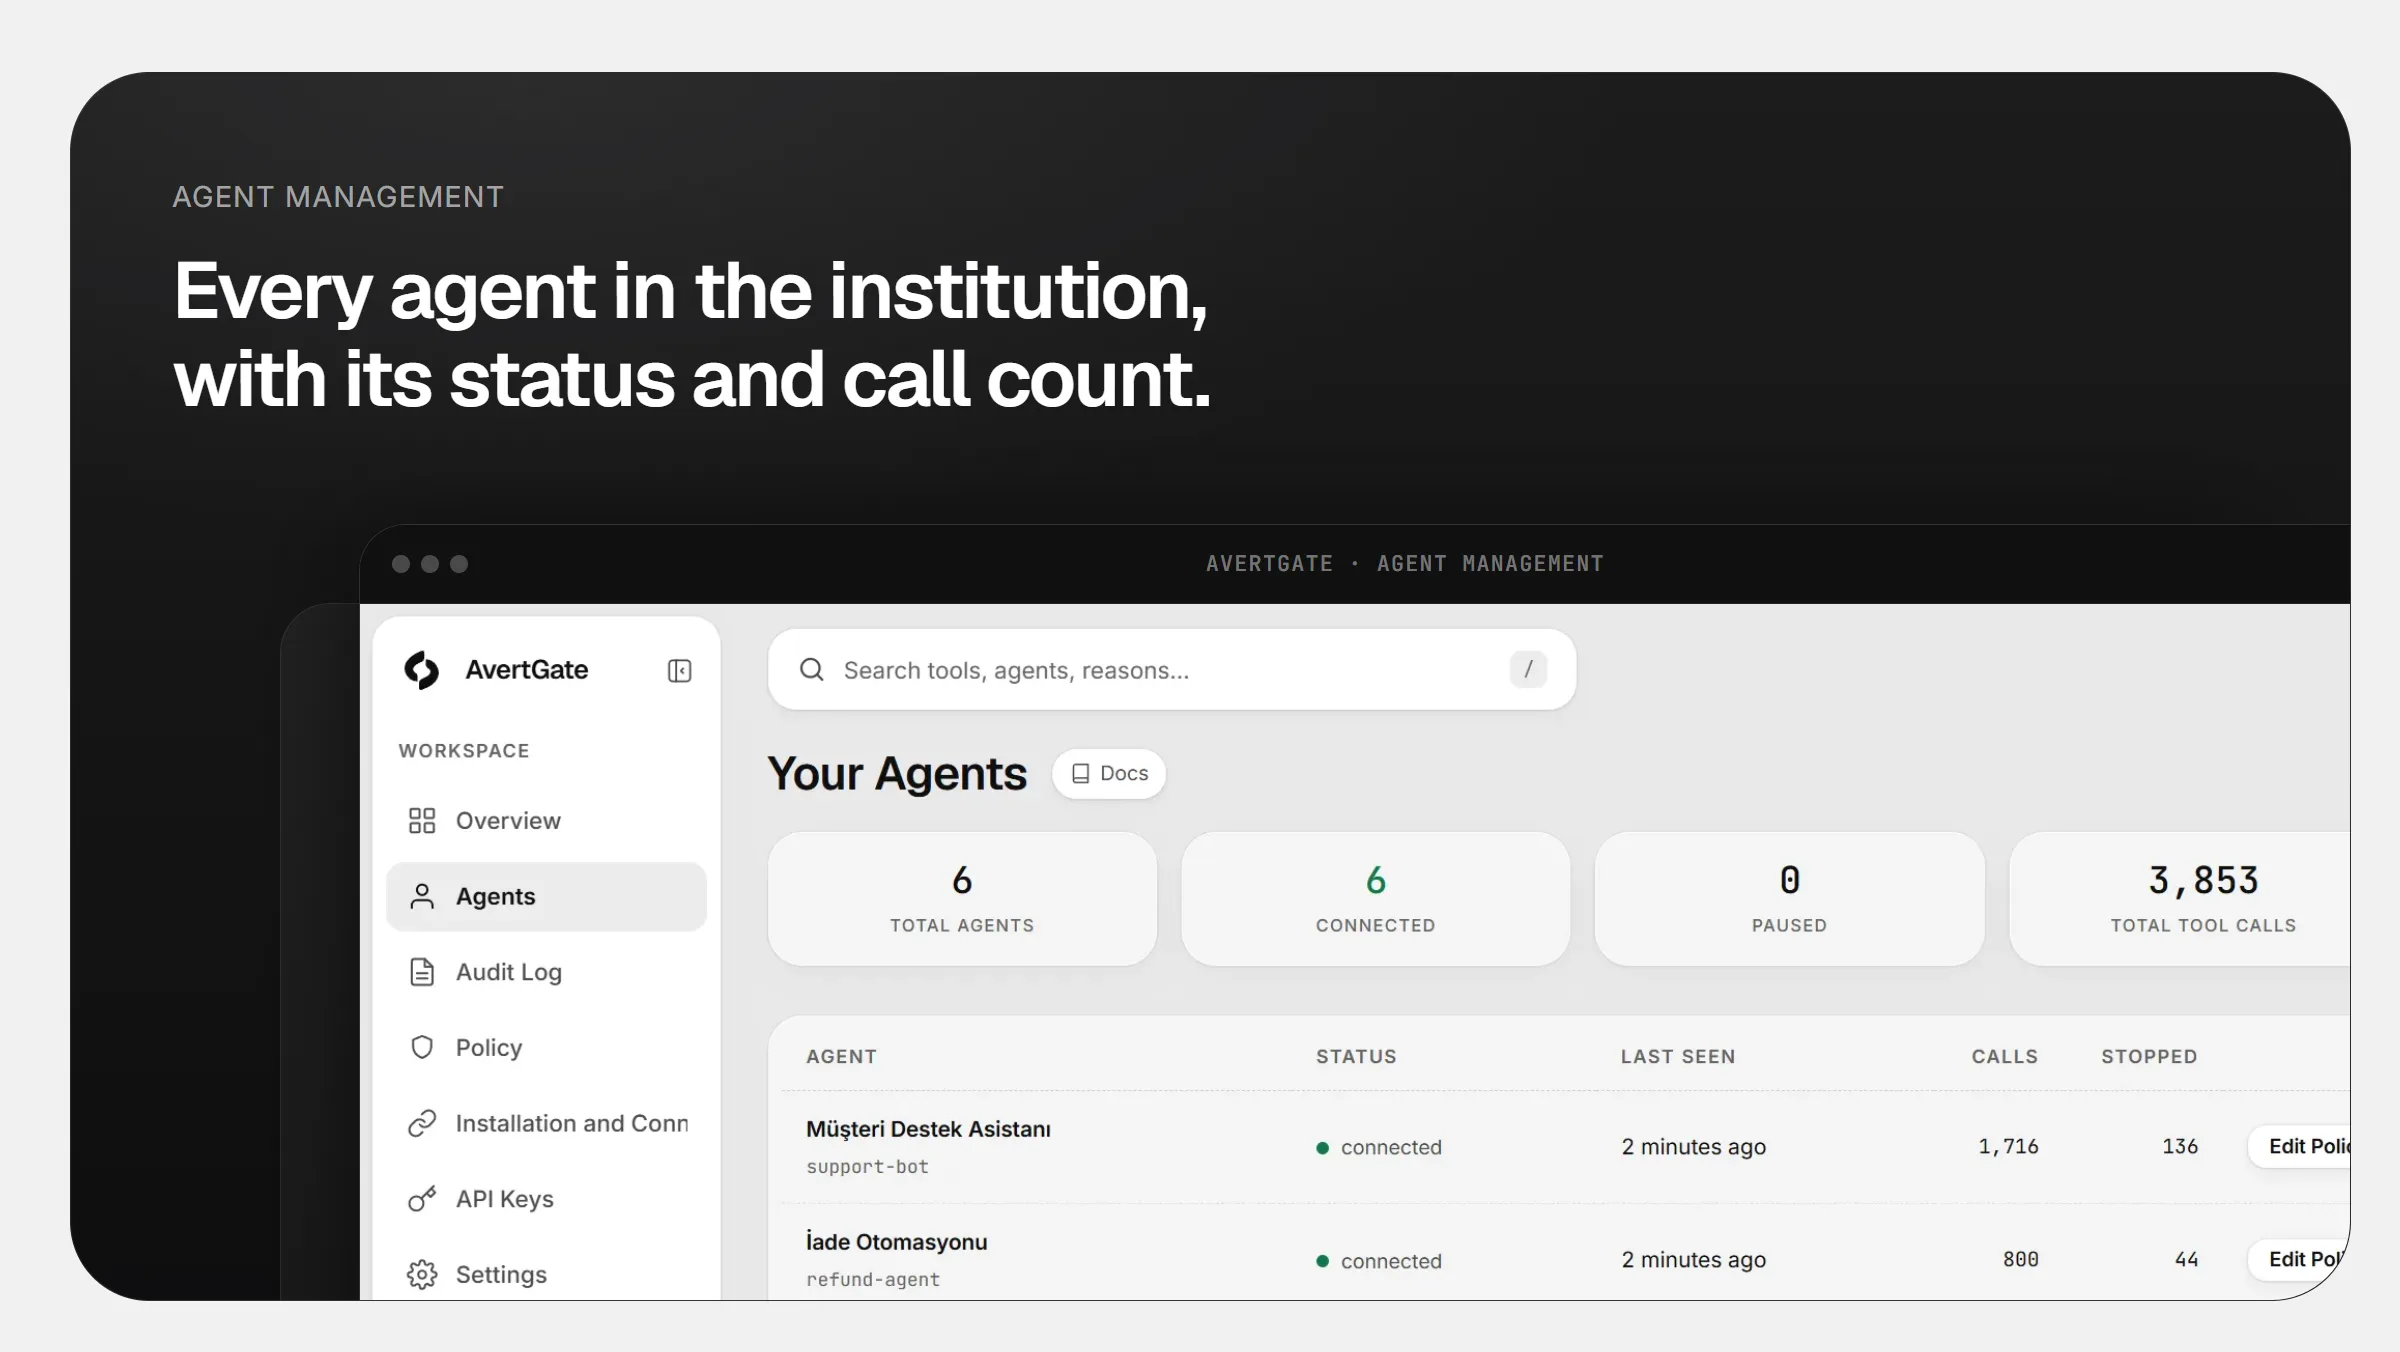
See everything a coding agent does in the terminal.
Files read, commands run and pushes made are gathered in one record stream.
- Every command on record with its arguments
- The whole flow between session start and end is traceable
- You show auditors records, not screenshots
- Test suite ranDeveloper machineInstant
- Production deploy requestedWaiting for manager approvalIn Slack
- Secret file read attemptedStopped by policyStopped
- Force push to a protected branch requestedStopped by policyStopped
Let the agent work in the terminal, and you draw the limit.
Tests and builds stay free. Production deploys go to approval; file deletion and force push never run.
- Rules per command and argument
- Above-threshold actions go to a manager
- A command that is not listed does not run
Keep secrets from leaving the machine.
If a file the agent read holds an API key or a password, it is masked before an outbound call or the call is stopped.
- Key and password patterns are scanned
- Outbound calls are masked or stopped
- Every finding goes on record
#developer-approvalsAvertGateAPP14:02
A coding agent wants to send a file out.
- File.env.production
- ReasonContains a secret key
Waiting for approval. Nothing is sent if rejected.
- ~4.2 msAverage added latency
- 100%Local isolation: data stays on your network
- ZeroChanges to agent code
Frequently asked
Does it work with Cursor, Copilot and Windsurf?
It works with coding agents that call tools over MCP or HTTP. The agent calls the same tools; the calls go through AvertGate.
Is our data sent to AvertGate?
No. The gateway runs on your network. Tool arguments, results and file contents never leave it; only redacted event data reaches the dashboard.
Do we have to change agent code?
No. The agent connects to AvertGate instead of the tool server; only the connection address changes. If the tool call path runs over MCP or HTTP, the same policy applies.
Take your agents to production with confidence.
Every rollout starts with a demo and a POC on your own agents.