An agent that touches patient data needs a gate.
Scheduling, results and billing agents reach sensitive records. AvertGate limits which tool may touch which record and stops the call that carries data out.
Decision flow
The query never reached the database
query_databaseDELETE FROM patients- Only SELECT is allowed
- Agent identity recognized
- Decision written to the record
A small mistake becomes a large breach.
Sending a patient record to the wrong recipient is a single tool call for an agent. Because no human looks at it, it is also noticed late.
Narrow access
The agent can call only the tools its job needs; a tool not on the list is denied.
Control the exit
On outgoing email and requests, data scanning and an allowed-recipient list apply.
Add human approval
Risky actions such as bulk export go to an authorized person for approval.
See it. Limit it. Prove it.
Example rules for a scheduling agent.
Reads are bounded, exports need approval, unapproved recipients are closed.
- Query limits. Only SELECT passes; destructive SQL such as DROP and DELETE is blocked.
- Recipient limits. Outgoing emails are limited to allowed domains.
- Local formats. Formats such as protocol or patient numbers are added to the policy as regex rules.
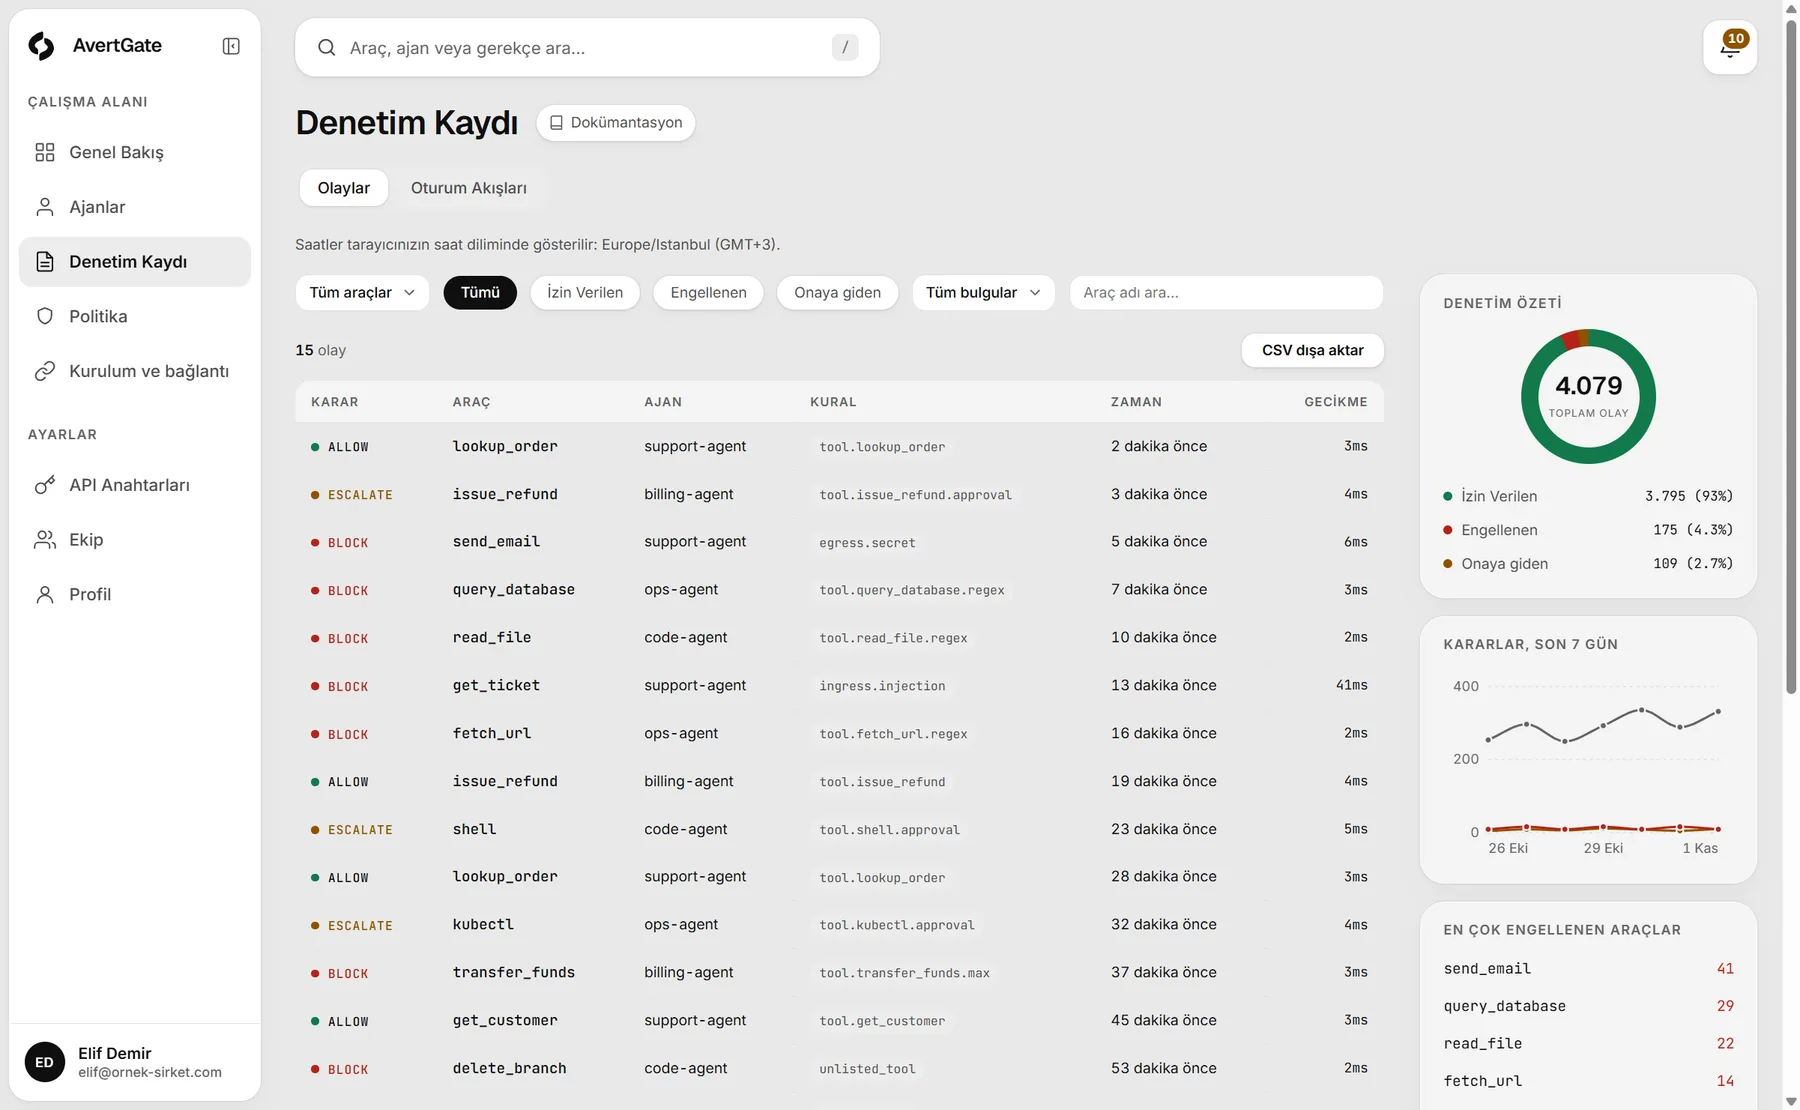
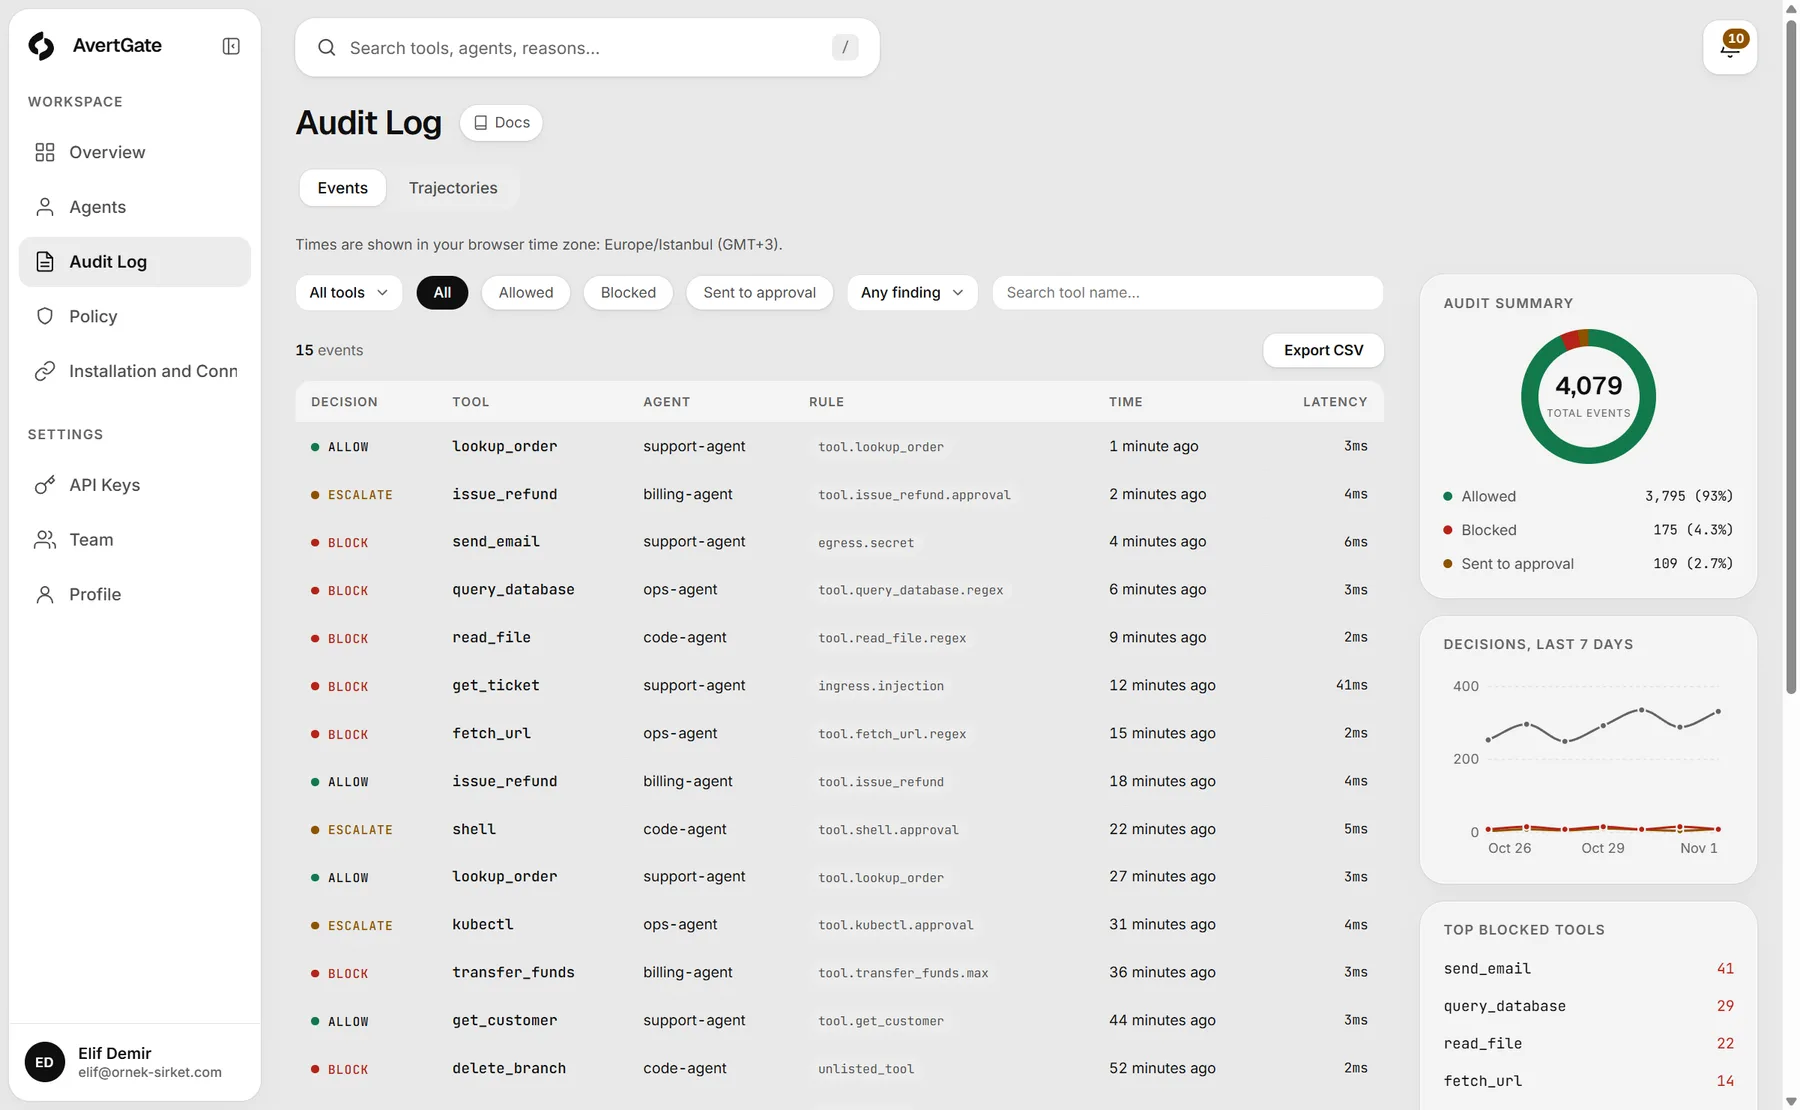
Audit trail
Every call in the live stream.
Take the rules out of code.
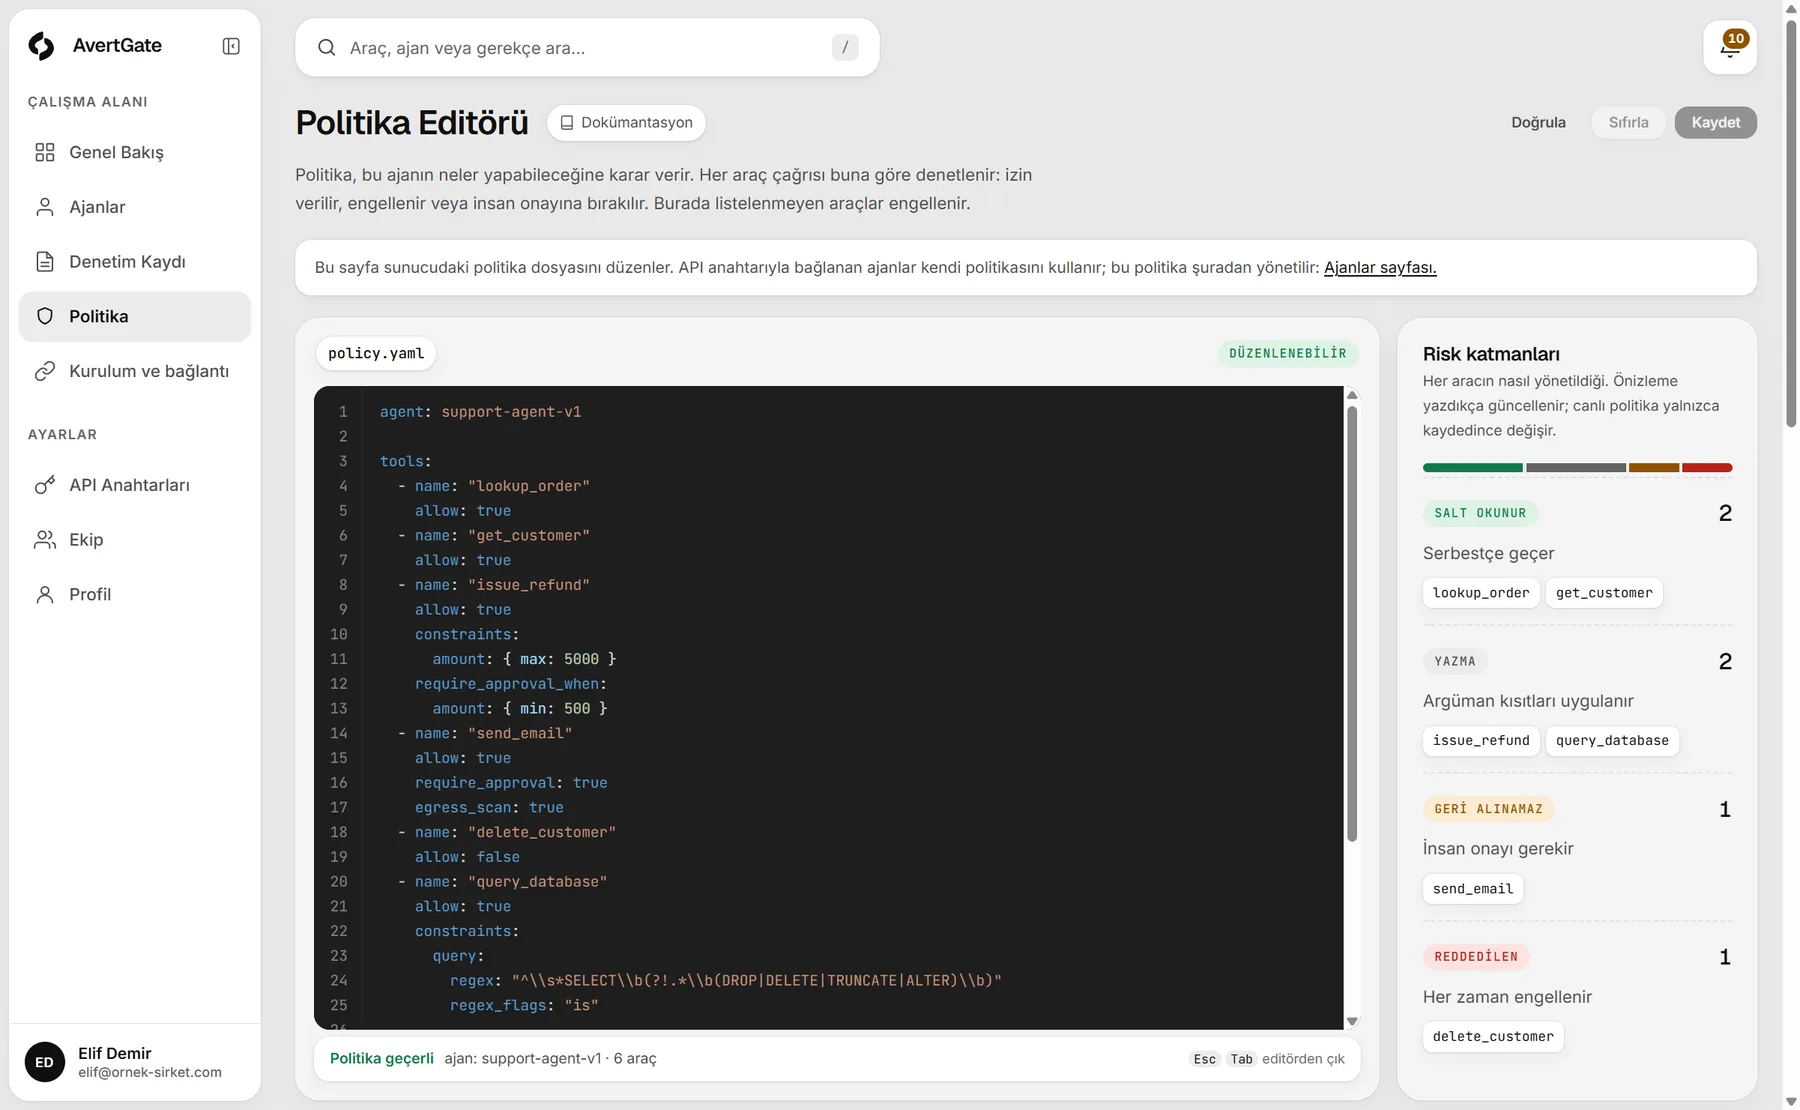
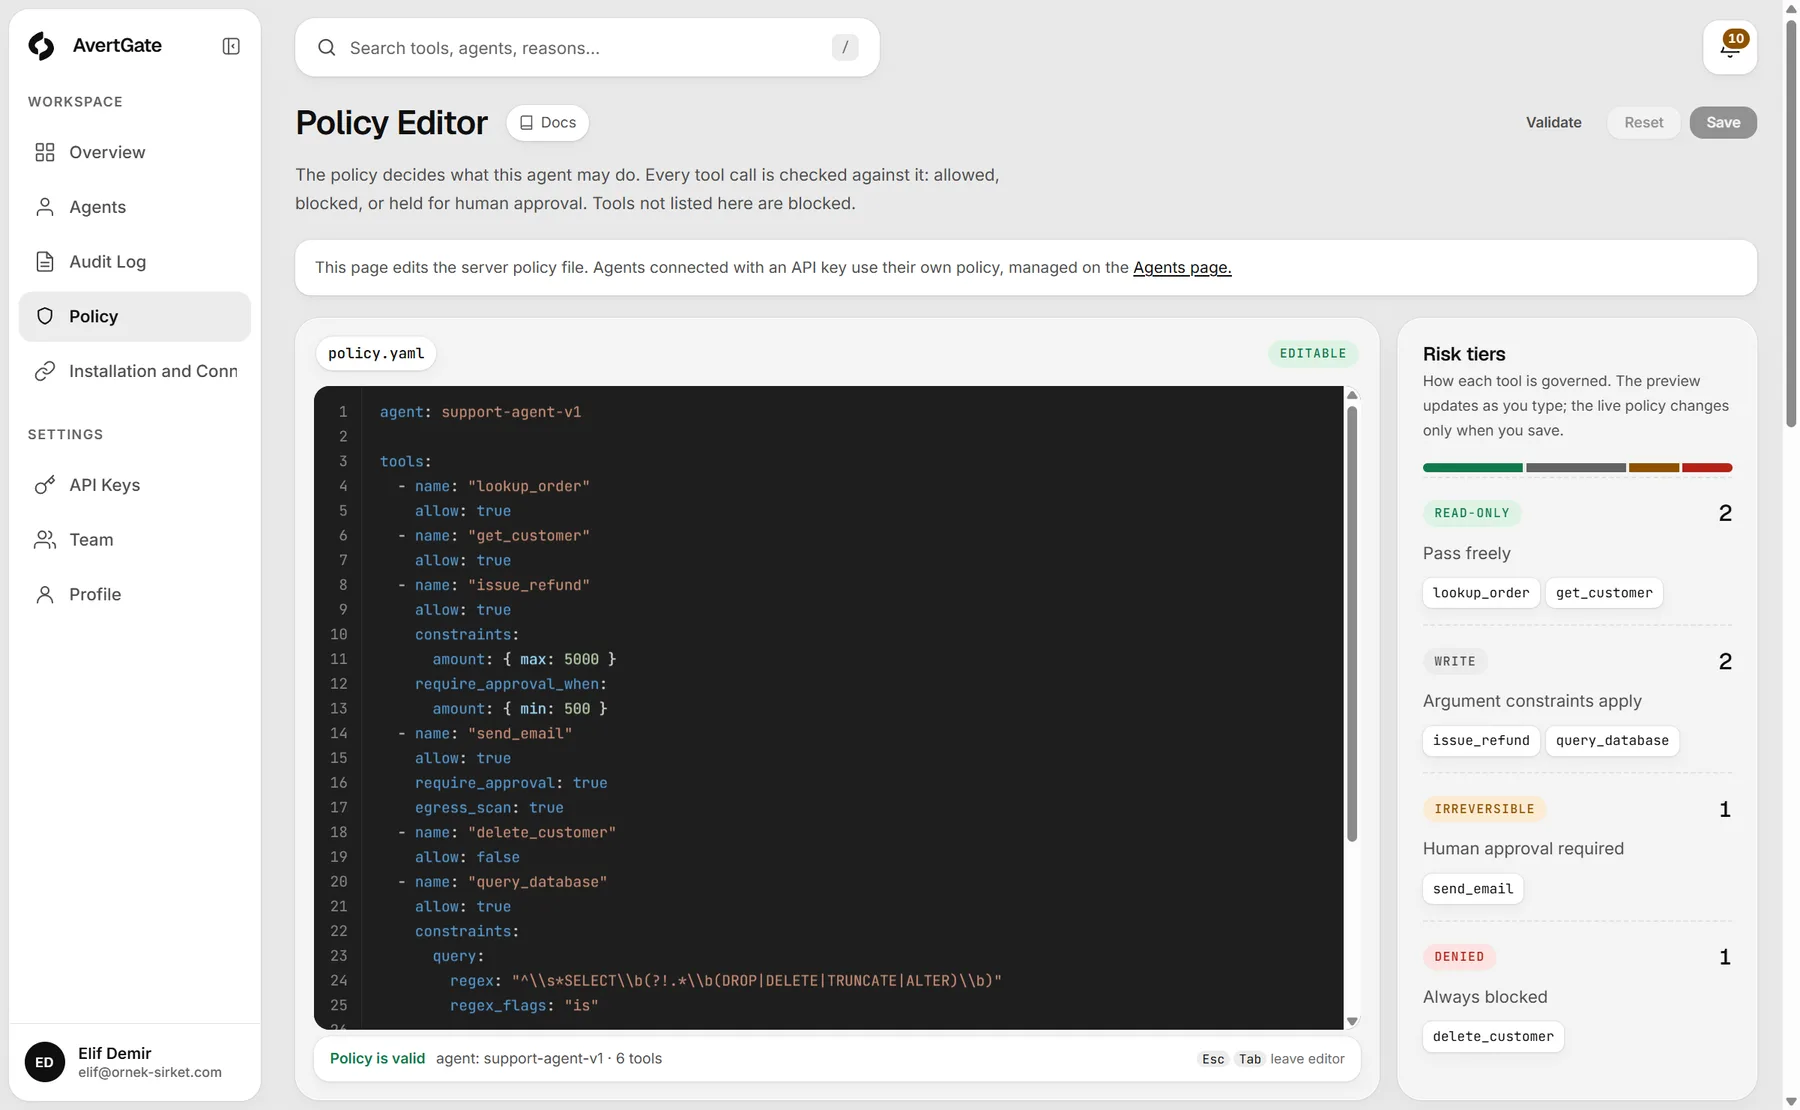
Allow, limit and approval rules per tool and argument live in a single YAML file. A change needs no redeploy.
- Deny by default. A tool that is not listed does not run.
- Argument limits. Fields such as amount, SQL and URL are bound to a rule.
- Human approval. Risky calls wait for approval in Slack.
Policy editor
The rule is written on one screen.
Every decision is recorded.
The decision, reason and rule id are linked with SHA-256; a record changed afterwards is detected.
- Reasoned decision. Every event carries the reason and rule id.
- Redacted arguments. Raw data never reaches the dashboard.
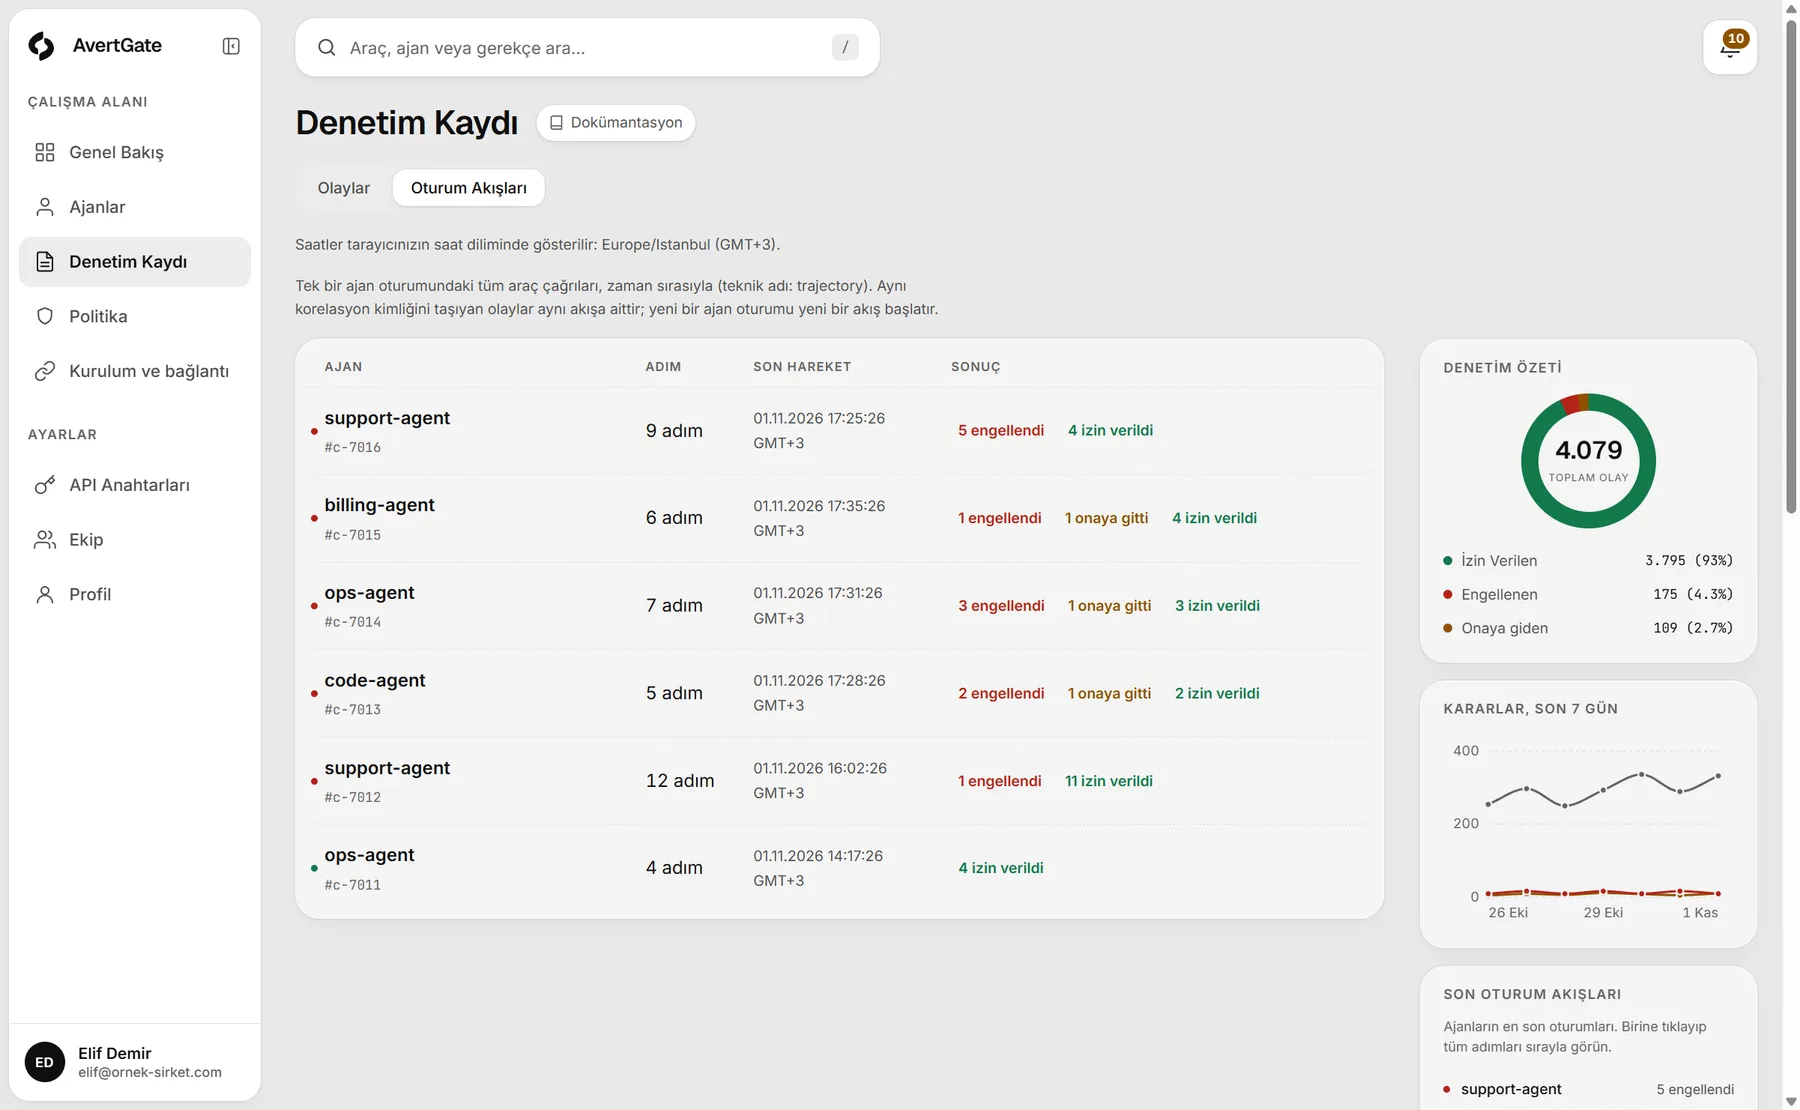
- Session trail. Calls in the same session are read together.
Session trails
Every session is traced end to end.
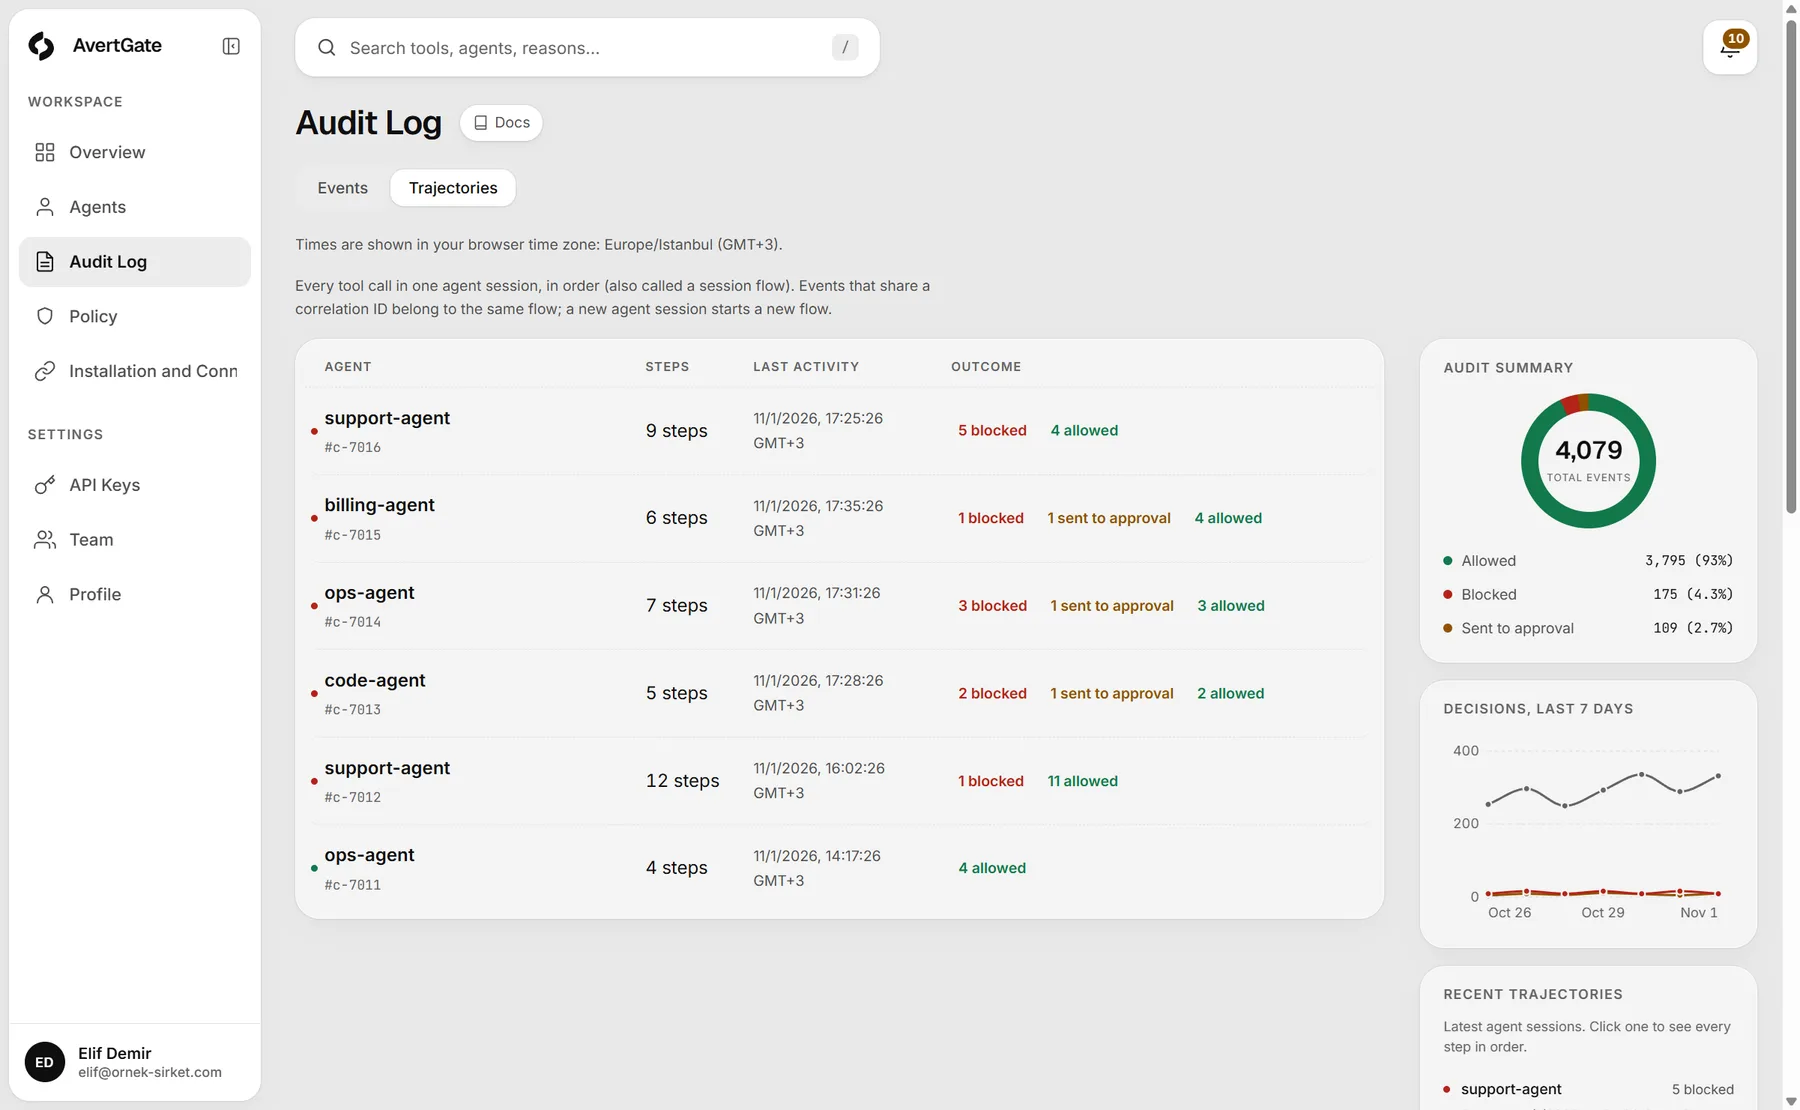
Audit trail
Review every call that touched a sensitive record.
Frequently asked
Is AvertGate HIPAA or healthcare-regulation compliant?
We make no such certification claim. We support your own compliance process by keeping health data in your network and recording every decision.
Does patient data go to the cloud?
No. Calls and results are processed in the Data Plane. Only redacted events go to the dashboard.
Do I have to use a cloud model?
No. For closed networks, local semantic inspection can be set up with Ollama or vLLM.
Guarantees
Four fixed principles behind every decision.
- 3 decisionsEvery call ends in allow, block or human approval.
- Fail-closedIf a check errors, the call is not run.
- SHA-256 chainEvents are chained, so any change after the fact is noticed.
- Your data stays with youTool calls and results never leave your network.
Put a gate in front of your agents.
Every deployment starts with a demo and a POC on your own agents.